Loading...

Supporting developers, startups, and full-fledged companies building on Stellar and Soroban
© 2026 Stellar Development Foundation
Subscribe to the Newsletter
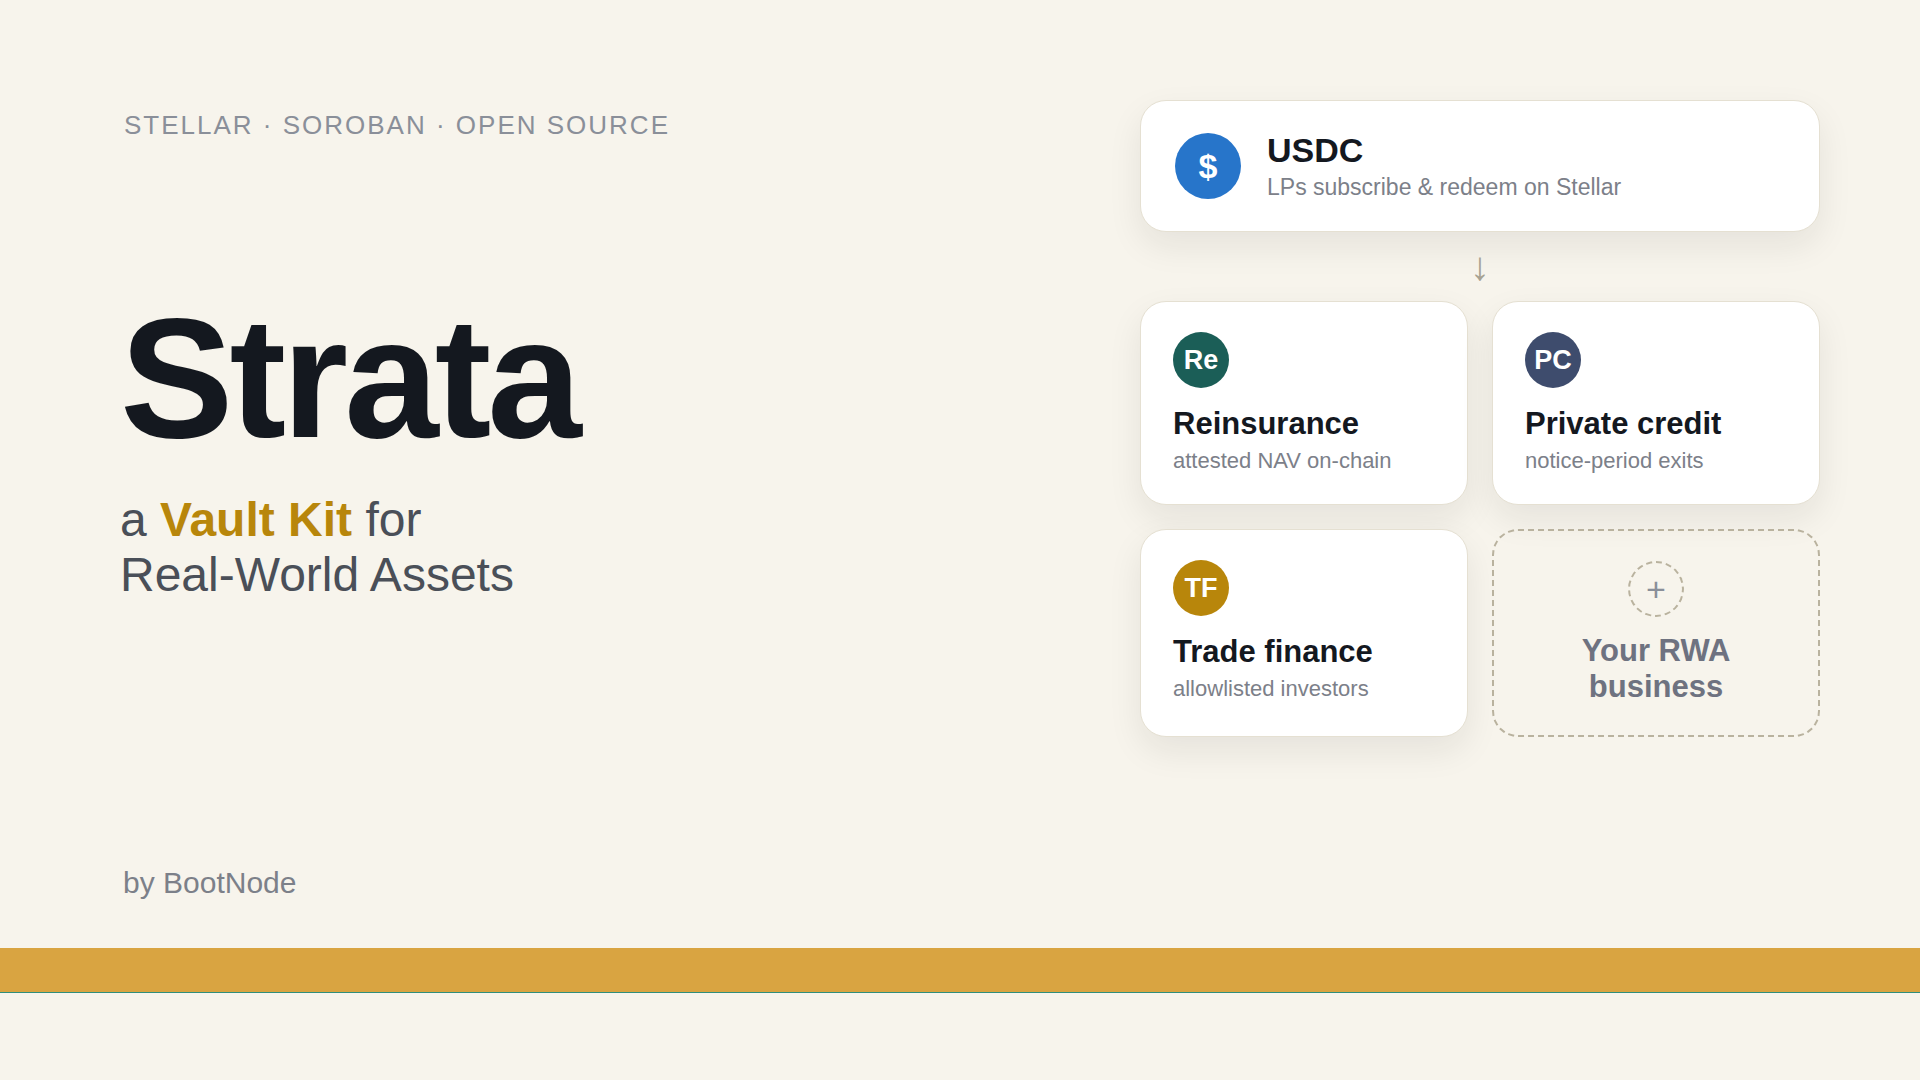
Teams building tokenized RWA products on Stellar today build the entire stack themselves. OpenZeppelin's library covers the standardized part: SEP-41 token, SEP-56 vault, allowlist, pausable, access control, and upgradeability. Everything that makes an RWA vault an RWA vault is left to each team: attested valuation with guardrails so a wrong or compromised report can't drain the vault, reconciling off-chain capital against the on-chain reserve, notice-period redemptions and a queue for when the reserve is short, separation of duties across reporting, funds movement, and compliance, and the operational surface to run it.
So, each team spends a large share of their budget rebuilding the same trust-critical code, widening their audit surface, and delaying GTM.
We propose building a configurable module that covers that layer, built on top of OpenZeppelin's primitives rather than replacing them. A team sets parameters and authorities and deploys. What stays theirs is their business: the legal structure, the valuation source, the attestation mechanisms, and the calibration values.

By Open RWA Vault Infrastructure
Strata, a Vault Kit for RWA